Decision guide
WebSocket vs REST vs FIX: Which Trading API to Use
Compare WebSocket vs REST vs FIX for trading APIs: session model, market data, order entry, recovery, and when each fits brokers, providers and funds.
Direct answer
WebSocket vs REST is a choice about who starts each exchange and how long the connection stays open. REST sends a request and gets a response, which suits reference data, account administration and reports. WebSocket keeps one two-way connection open for pushed updates. FIX is a trading messaging standard with its own session rules. No protocol is universally faster.
Key takeaways
- WebSocket vs REST is mainly about who starts the exchange and how long the connection stays open, not which one is faster.
- REST suits request-response work such as reference data, account administration and reports. Order commands need idempotency and status checks.
- WebSocket suits pushed streams, but the application must own subscriptions, sequencing and reconnect rules.
- FIX is a standard trading messaging protocol with a session layer. Counterparties still agree dialects, certification and operating procedures.
- No interface is universally fastest. Measure the full path and rehearse recovery before choosing.
- Orrnn's public RTX5 REST and WebSocket APIs are labelled Planned and its FIX adapters have no published build yet, so treat this guide as protocol education.
WebSocket vs REST vs FIX at a glance
The table compares the three interfaces on the questions that usually decide the design. Use it as a starting point, then test the counterparty's actual specification.
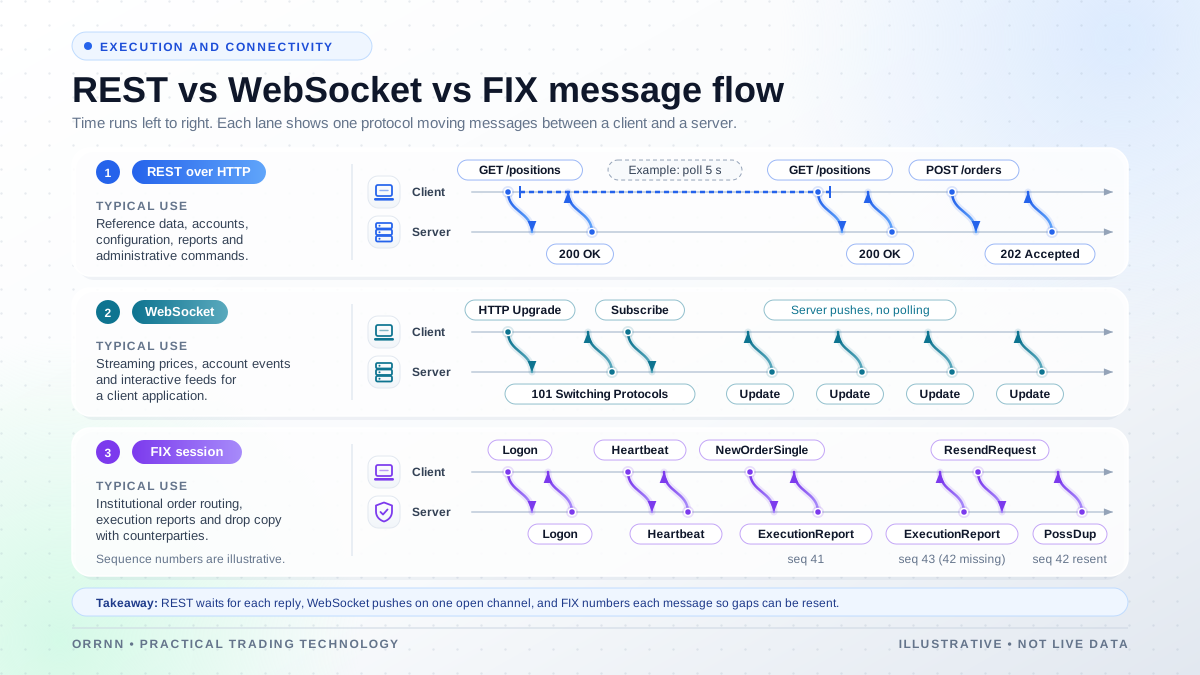
WebSocket and REST are API transport styles. FIX is a standardized financial messaging protocol with a session layer. Comparing them only on speed hides the differences that matter in production: who starts each exchange, how long the connection lives, how orders are identified, and how a client recovers after a gap.
Typical characteristics, not guarantees
| Question | REST over HTTP | WebSocket | FIX |
|---|---|---|---|
| Session model | Independent request and response pairs. Each call normally stands alone. | One HTTP upgrade handshake, then a persistent two-way channel defined by RFC 6455. | Logon, heartbeat, logout and sequence numbers defined by the FIX session layer. |
| Connection lifetime | Per request. Connections may be reused under HTTP keep-alive. | Stays open until either side closes it or the network drops. | Usually a long-lived session kept open through the trading day, as agreed with the counterparty. |
| Market data | Snapshots on request. Polling is usually inefficient for fast-changing prices. | Subscribe once, then receive pushed updates. Snapshot and delta handling is up to the provider. | Market data request messages, with snapshot and incremental refresh messages. |
| Order entry | Commands to order resources. The outcome may arrive later, so status queries are needed. | Provider-defined order messages. No shared trading vocabulary across providers. | Standard message types such as new order, cancel, cancel-replace and execution report. |
| Ordering and recovery | No built-in message sequence. Recovery relies on identifiers and state queries. | Ordered within one connection only. Gaps after a reconnect must be handled by the application. | Sequence numbers, gap detection and resend requests defined by the session protocol, subject to agreed policy. |
| Typical use | Reference data, accounts, configuration, reports and administrative commands. | Streaming prices, account events and interactive feeds for a client application. | Institutional order routing, execution reports and drop copy with counterparties. |
| When to choose | Request-response work at modest frequency, or where tooling and auditability matter most. | Server-to-client streams and bidirectional messages where a persistent channel pays off. | Counterparty or institutional flows that already specify FIX, or where standard trading messages are required. |
Separate the transport from the trading contract
Protocol comparisons often mix several layers: network transport, connection lifecycle, message representation, business vocabulary, session recovery, authentication, and counterparty operating procedures. FIX defines a family of standards for financial messages and, in common session-based deployments, conventions for sequencing and recovery. REST describes an architectural style commonly implemented over HTTP. WebSocket defines a protocol for two-way communication over a persistent connection. None alone specifies the entire trading service.
Two APIs can both be called FIX or REST and remain materially incompatible. A venue may require custom FIX tags, specific order-state transitions, a certification script, and a particular session schedule. REST APIs may use different resources, identifiers, error models, idempotency rules, or pagination. WebSocket feeds may differ on subscription limits, snapshots, deltas, ordering, and reconnect behavior. Always evaluate the actual specification and environment.
Start from workflows: reference data, account administration, historical queries, market-data subscriptions, order entry, execution reports, drop copy, positions, reporting, and operational controls. For each, define timeliness, throughput, delivery and ordering expectations, recovery, audit, security, and who operates both ends. Then select or combine interfaces.
Understand the characteristic strengths and costs
FIX can reduce ambiguity between experienced financial counterparties because it provides established message models and practices, but implementation still requires bilateral agreement. Session operations, certification, message stores, sequence gaps, calendars, and production support add complexity. FIX is not automatically faster than every alternative, and text FIX over TCP is only one member of a broader standards family.
REST benefits from widespread tooling, inspectability, HTTP infrastructure, and a natural fit for resources and request-response operations. It can submit orders, but the design must address duplicate requests, asynchronous status, timeouts after ambiguous outcomes, rate limits, and event delivery. Polling a REST endpoint for rapidly changing market data is usually less efficient than a purpose-built stream.
WebSocket avoids opening a new connection for every update and supports server-to-client and client-to-server messages after the handshake. The application still needs an envelope, authentication lifecycle, heartbeats, flow control, sequence or version information, recovery, and state reconciliation. A connected socket is not proof that every event has been processed.
Typical characteristics, not guarantees
| Interface | Often useful for | Design questions that remain |
|---|---|---|
| FIX | Order routing, execution reports, drop copy, institutional counterparty flows | Version/dialect, messages, custom fields, sequencing, recovery, certification, session operations |
| REST over HTTP | Reference data, accounts, configuration, reports, low-frequency commands | Resources, idempotency, status/error semantics, rate limits, pagination, consistency, async completion |
| WebSocket | Market-data streams, event updates, interactive bidirectional messaging | Subscriptions, ordering, heartbeat, backpressure, snapshots, gaps, reconnect, resynchronization |
Choose interfaces by workflow
Reference data and configuration often map cleanly to REST resources because consumers can retrieve current state, use caching controls where appropriate, and make auditable changes. Bulk operations may need asynchronous jobs rather than long-running HTTP requests. Responses should distinguish accepted work from completed work and provide a stable operation identifier for follow-up.
Order routing requires unambiguous identifiers, state transitions, validation, duplicate prevention, cancellation or replacement rules, and recovery after uncertain responses. FIX offers familiar conventions for many institutional flows. A well-designed REST or WebSocket order API can also work, but the provider must document the same business semantics. The choice may be constrained by counterparties and existing certification rather than greenfield preference.
Market data usually needs a streaming interface. A common pattern uses REST for instrument discovery and snapshots, then WebSocket for incremental updates. Consumers need to know whether a stream is conflated, the meaning of sequence numbers, how to detect a gap, how to obtain a fresh snapshot, whether updates are per instrument or channel, and how slow consumers are handled.
Drop copy, positions, and reports can use different channels depending on timeliness and audit needs. Do not treat a live event stream as the sole durable record. Define how the consumer reconstructs state, how corrections appear, and which query or report is authoritative when events and current-state endpoints disagree.
Decision guide for brokers, liquidity providers and funds
Each role faces the same three protocols with different constraints. Decide each boundary separately rather than choosing one protocol for the whole stack.
A broker may use all three interfaces at once. A client platform might stream prices over WebSocket, expose account administration over REST, and connect to a liquidity provider or prime broker over FIX. Each boundary has its own counterparty, identifiers and recovery path, so a choice made for one boundary rarely settles the others.
Liquidity providers and venues usually specify their own FIX dialect, certification steps and session schedule. For them, the practical question is which interfaces their counterparties accept and what they must certify, not which protocol is most modern. Ask for the message matrix before estimating effort.
Funds and trading teams need order routing, execution reports and allocation data that survive restarts and disconnects. Check whether the OMS or EMS already supports the chosen protocol, and identify which store is authoritative when a stream and a current-state query disagree.
Before choosing, answer these questions in writing:
- Which counterparties must you connect to, and which protocols and dialects do they accept?
- Which events must be recoverable without a human operator?
- What is the authoritative source when an event stream and a state query disagree?
- Who operates each end of the connection, and what support hours apply?
Design identifiers, idempotency, and ambiguous outcomes
Every order or command should have a client-generated identifier with a documented uniqueness scope and retention period. The server should explain what happens when an identifier is reused with identical or different content. HTTP idempotency depends on application behavior as well as the method name; a network timeout can leave the client uncertain whether a request was processed. Retrying blindly can duplicate economic intent.
After a timeout, the client needs a recovery path: query by client identifier, receive the resulting event, or reconcile through another authoritative channel. FIX workflows similarly depend on identifiers and execution reports, while session resends address message delivery rather than automatically resolving every business ambiguity. Document which identifier remains stable across replace, cancel, partial fill, venue routing, and internal systems.
Maintain a state machine rather than inferring state from the last response received. Validate impossible transitions and preserve the raw message or trace needed for investigation under appropriate controls. Time stamps help analysis but should not be the only ordering mechanism; clocks differ and events can be buffered or retransmitted.
Make sequencing and recovery explicit
For every stream, state whether ordering is global, per connection, per account, per instrument, or not guaranteed. Define the sequence type, reset behavior, wrap or persistence rules, and whether filtered messages create apparent gaps. Consumers should know when they can replay, when they must request a snapshot, and how to prevent old buffered events from corrupting newer state.
FIX session sequencing provides mechanisms for detecting and requesting missing messages, but counterparties must agree operational policies and message-store behavior. Gap fills and resend requests need careful handling, and duplicate flags do not remove the need for business-level idempotency. Operators require procedures for reset, disaster recovery, and simultaneous reconnects.
A WebSocket API needs its own recovery contract. Include heartbeat or liveness expectations, disconnection detection, authentication refresh, exponential backoff or server guidance, resubscription, snapshot-plus-delta sequencing, and limits on replay. REST endpoints can support recovery by exposing current state and history, but consistency and pagination boundaries must be understood.
Checklist
- Ordering scope and sequence semantics documented
- Gap detection, replay limits, and snapshot recovery tested
- Duplicate and stale messages handled safely
- Reconnect and authentication-refresh behavior defined
- Authoritative state source identified for reconciliation
- Operator procedures cover resets, extended outages, and disaster recovery
Plan capacity, backpressure, and latency measurement
Capacity starts with message size, burst rate, subscription count, connection count, processing cost, and downstream fan-out. Average rates hide the bursts that matter around market events or session boundaries. Agree provider limits and client behavior when they are reached. A stream should define whether it buffers, drops, conflates, disconnects, or signals a slow consumer.
Measure latency at named points using synchronized clocks or within a single clock domain. Separate network round-trip time, server processing, queueing, serialization, client receipt, and strategy processing. Report distributions and tail values over an adequate period, not one best observation. Results from a test endpoint or quiet market should not be presented as production guarantees.
Protocol overhead is only one contributor. Connection placement, TLS, proxies, message size, encoding, garbage collection, event loops, queues, risk checks, venue path, and application logic may dominate. Optimize after measurement. Binary encodings or persistent channels can reduce some costs, but they also change tooling and operational complexity.
Integration effort and failure modes
Integration effort usually comes from the counterparty and the documentation, not the protocol name. Expect time for specification review, sandbox access, certification scripts, credential and certificate setup, and reconciliation of test results. The same protocol can produce very different effort depending on how complete the documentation and test access are.
Plan for operation after go-live as well. Monitoring, reconnect procedures, key rotation, version changes, and support escalation all add cost. The failure modes below are the ones most often missed in early designs. Each links back to the detailed guidance above.
- A timed-out REST order retried without a stable client identifier can create a duplicate instruction. See identifiers and ambiguous outcomes above.
- A WebSocket client that reconnects and resumes from the latest update can miss events if no snapshot or replay rule exists. See sequencing and recovery above.
- A FIX sequence gap or a long resend request can delay execution reports while the session catches up.
- An expired certificate or a rotated key can stop every interface at once. Put certificate and key expiry in the runbook.
- Rate limits or burst rejections can refuse commands during fast markets. Agree limits and back-off behavior before production.
Secure the full connection lifecycle
Use current encrypted transports and validate peer identity. Store credentials in an appropriate secrets system, scope permissions, rotate keys, and avoid placing reusable secrets in URLs or logs. Define whether authentication is per connection, request, message, user, application, account, or combination. Long-lived connections need a documented refresh and revocation behavior.
Network allowlists can reduce exposure but are not a substitute for strong identity and authorization. Enforce authorization at the business object: an authenticated session should not be able to access another account by changing an identifier. Signatures and nonces may be appropriate for some APIs, but their canonicalization, clock tolerance, replay protection, and key recovery must be testable.
Logs should support investigation without leaking credentials, full personal data, or sensitive strategy information. Define correlation identifiers across gateway, risk, order, execution, and downstream services. Monitor authentication failures, unusual subscriptions, limit responses, reconnect storms, sequence gaps, and denied operations with thresholds that operators can act on.
Test the contract, not only connectivity
A conformance pack should cover every supported message or resource, required and optional fields, boundary values, precision, time zones, enumerations, unknown fields, malformed input, unsupported operations, permissions, and business-state transitions. Use deterministic cases and preserve versions. Certification with a counterparty is valuable but does not replace internal regression tests.
Add failure and recovery tests: duplicate requests, delayed acknowledgements, partial responses, timeouts after acceptance, sequence gaps, dropped connections, stale DNS, expired certificates, key rotation, server restart, rate limiting, slow consumer, and replay exhaustion. Verify that the client does not convert uncertainty into duplicate orders or silently stale state.
Sandbox behavior must be documented. Many test environments use different liquidity, market hours, data rates, risk rules, certificates, or capacity. Record what the sandbox cannot prove and arrange targeted production-readiness checks. Version compatibility should include a deprecation window, change log, test environment, and consumer inventory.
Use hybrid patterns deliberately
A common design uses REST for discovery, current-state queries, administrative actions, and recovery; WebSocket for streaming market or account events; and FIX for institutional order and execution flows. This can align each interface with its strengths. It can also create three identity models, identifiers, versions, and support paths unless the provider designs them as one coherent contract.
Define cross-channel consistency. If an order is submitted through FIX, can it be queried through REST and observed through WebSocket using the same identifiers? Which channel is authoritative during a disagreement? How long can one representation lag another? Can a client safely switch recovery channel during an outage? These questions are more important than whether each interface works independently.
A gateway or internal canonical model can isolate applications from counterparty differences, but it becomes critical infrastructure. It must preserve semantics, identifiers, precision, ordering, raw evidence, and error detail rather than reducing every venue to the least common denominator. Test mappings whenever either side changes.
Decision checklist and limitations
There is no protocol that is universally fastest, safest, or best for trading. Results depend on implementation, topology, counterparty, workload, controls, and operational competence. This guide is technical education rather than a promise about Orrnn products or a substitute for security, architecture, compliance, or counterparty review. Test the exact interfaces and versions you intend to use.
Orrnn's public RTX5 REST and WebSocket APIs are labelled Planned, and the RTX5 roadmap lists the FIX 4.4 and 5.0 adapters as build not published (checked 9 November 2026). Nothing in this guide states that any RTX5 API described here is available. For the build you evaluate, request the released specification, authentication model, supported endpoints and acceptance test results.
Checklist
- Workflows and business semantics defined before selecting an interface
- Actual provider version, dialect, schemas, limits, and support model reviewed
- Identifiers, idempotency, state transitions, ordering, and recovery tested
- Capacity model includes bursts, slow consumers, reconnects, and downstream processing
- Security covers transport, identity, authorization, secrets, rotation, revocation, and logs
- Sandbox differences and production-readiness evidence recorded
- Cross-channel consistency and the authoritative state source are explicit
- Operators have runbooks and monitoring for gaps, limits, failures, and changes
Frequently asked questions
What is the difference between WebSocket and REST?
REST is a style for resource-oriented APIs over HTTP. The client sends a request and receives a response, and each call usually stands alone. WebSocket starts with an HTTP handshake and then keeps one connection open so either side can send messages. REST suits commands, reference data and reports. WebSocket suits continuous updates such as prices, but the application must handle reconnects, ordering and state.
Is FIX faster than WebSocket?
Not as a general rule. FIX and WebSocket are different kinds of interface, and measured speed depends on the network path, server processing, message size, the venue and the application code. Protocol overhead is only one contributor. Measure latency at named points for the exact endpoints you plan to use, and treat any speed claim as untested until you can reproduce it.
Can you place orders over REST?
Yes, many trading APIs accept orders over REST, but the design must handle what HTTP does not solve for you. A timeout can leave the client unsure whether an order was accepted, so the client needs a unique identifier, a documented duplicate rule and a way to query the outcome. Confirm how the provider reports accepted versus completed status, and how cancels and replacements are identified.
When should you use WebSocket for market data?
Use WebSocket when a client needs pushed updates after a subscription rather than repeated polling. A common pattern loads instrument details and an initial snapshot over REST, then applies incremental WebSocket updates. Before production, confirm the sequence or version fields, how a gap is detected, how a fresh snapshot is requested, and how slow consumers are handled.
Do brokers need FIX?
Not always. A broker needs whichever interfaces its counterparties, platform and operations require. FIX is common for institutional order routing, execution reports and drop copy, and some liquidity venues or prime brokers may require it. Client-facing functions often use vendor or platform APIs. Ask each counterparty for its supported protocol, dialect and certification requirements before design starts.
Primary sources and further reading
These sources support the frameworks and definitions used in this guide. They do not endorse Orrnn or establish that any product complies with the referenced material.
- FIX standards and technical resources
FIX Trading Community
Primary source for FIX standards; production connections may use versions, extension packs, or bilateral dialects.
- HTTP Semantics — RFC 9110
RFC Editor
The standards-track reference for HTTP semantics, including methods, status codes, and representation behavior.
- The WebSocket Protocol — RFC 6455
RFC Editor
The standards-track protocol specification for WebSocket framing, opening handshake, and connection behavior.
- OAuth 2.0 Security Best Current Practice — RFC 9700
RFC Editor
Current security guidance for OAuth 2.0 deployments where OAuth is part of the chosen API identity model.
Related reading
Broker platform migration
Apply interface sequencing, certification, and recovery requirements during a platform move.
Read →Measure broker-server latency
Build a measurement plan that separates network, protocol, server, and application delay.
Read →Algorithmic trading overview
Review Orrnn's algorithmic-trading overview separately from this protocol-neutral guide.
Read →FIX 4.4 vs latest FIX
Compare FIX 4.4 with later FIX versions before fixing a connectivity specification.
Read →Broker back-office controls
Design the controls that must reconcile orders, cash and positions across every interface.
Read →What Is FIX Protocol?
FIX sessions, message anatomy, common message types and versions in use.
Read →